
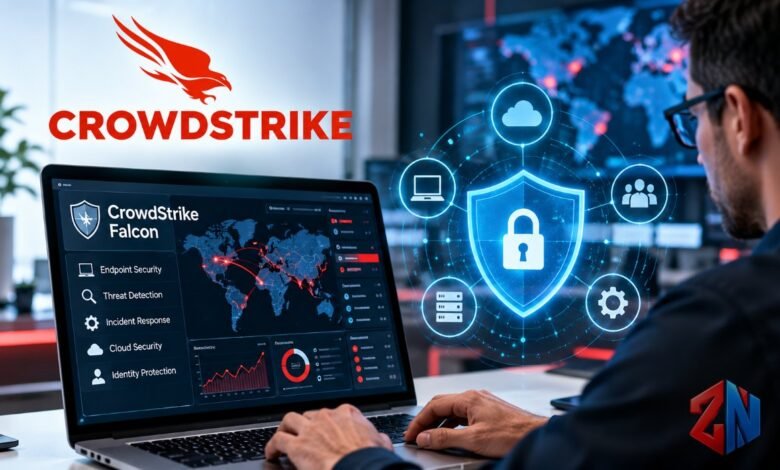
CrowdStrike is a major cybersecurity company that helps businesses protect computers, servers, cloud environments, and digital identities from cyberattacks. Its Falcon platform uses artificial intelligence, behavioral analysis, and threat intelligence to identify suspicious activity and respond to potential security breaches.
The company attracted worldwide attention following a major technology outage in July 2024. However, its role in cybersecurity extends far beyond that incident. Today, its technology supports organizations seeking protection against ransomware, malicious software, identity attacks, and increasingly sophisticated digital threats.
Understanding how its technology works is useful for business owners, IT professionals, and anyone interested in modern cybersecurity. This guide explores its background, Falcon security products, pricing, the global outage, and its position in the cybersecurity industry in 2026.
What Is CrowdStrike?
CrowdStrike Holdings, Inc. is an American cybersecurity company founded in 2011. Headquartered in Austin, Texas, it develops security technologies designed to detect, investigate, and prevent cyberattacks across business computing environments.
George Kurtz, a cybersecurity entrepreneur and former McAfee executive, is the company’s co-founder and chief executive officer. The business is publicly traded on the Nasdaq stock exchange under the ticker symbol CRWD.
Unlike security providers focused mainly on traditional antivirus software, the company offers a broader range of protection services. These include endpoint security, threat hunting, identity protection, cloud security, and incident response.
Its main product is the Falcon platform, which combines security capabilities through a centralized management system. Organizations can select different products and services according to their needs rather than managing every security function through a completely separate system.
This approach aims to make cybersecurity more manageable while improving visibility into potential threats.
How Does the CrowdStrike Falcon Platform Work?
The CrowdStrike Falcon platform combines endpoint monitoring, automated threat detection, and cloud-based security analysis. An endpoint is any device connected to a business network, such as a laptop, desktop computer, or server.
A lightweight software component called the Falcon sensor is installed on supported devices. It monitors relevant system activity and helps identify unusual behavior that may indicate an attack.
For example, if ransomware attempts to encrypt company files, Falcon may recognize suspicious activity and take preventive action before the attack spreads.
The platform uses several connected technologies to provide protection. Machine learning helps identify malicious behavior, threat intelligence provides information about known attackers, and cloud-based analysis supports investigations.
Some protection functions operate directly on devices, while cloud connectivity enables centralized monitoring and deeper analysis.
This combination allows security teams to investigate threats across multiple systems without relying entirely on traditional virus signatures.
Key CrowdStrike Security Features
The company’s cybersecurity services extend beyond basic malware detection. Its products address different stages of an attack, from initial prevention to investigation and recovery.
Next-Generation Antivirus Protection
CrowdStrike Falcon Prevent provides next-generation antivirus protection against malware, ransomware, and other malicious activity.
Traditional antivirus tools often rely heavily on identifying previously discovered threats. Modern protection uses additional techniques, including machine learning and behavioral analysis, to recognize suspicious activity.
This helps organizations defend against both familiar threats and previously unidentified attack techniques. However, no antivirus product can guarantee complete protection against every possible attack.
Endpoint Detection and Response
CrowdStrike EDR technology provides continuous visibility into endpoint activity.
Falcon Insight XDR can detect suspicious behavior, support investigations, and help security teams respond to attacks. XDR, or extended detection and response, brings together security information from multiple sources.
For example, if an attacker gains access to an employee’s computer, security teams may investigate suspicious processes, examine related activity, and isolate the affected device when necessary.
These capabilities can reduce the time between detecting an intrusion and taking action.
Cloud and Identity Security
CrowdStrike cloud security helps organizations monitor cloud workloads, identify security weaknesses, and detect threats affecting cloud infrastructure.
Identity protection addresses attacks involving compromised accounts, stolen credentials, and unauthorized access.
These functions matter because attackers do not always need to install malware. Some exploit legitimate accounts or poorly configured systems to enter business networks.
Threat Intelligence and Hunting
CrowdStrike threat intelligence provides information about cybercriminal groups, their tactics, and emerging attack methods.
Threat hunting involves actively searching for signs of malicious activity that automated systems might not immediately identify.
This approach helps security professionals understand not only whether an attack occurred but also how an attacker may have entered a network.
Managed Detection and Response
CrowdStrike Falcon Complete provides managed detection and response, commonly called MDR.
This service combines security technology with professional monitoring, investigation, and response capabilities.
Organizations without large internal security teams may find managed protection useful because cybersecurity specialists can help investigate and contain threats around the clock.
The exact protection and response responsibilities depend on the purchased service.
CrowdStrike vs Traditional Antivirus Software
The main difference between CrowdStrike and traditional antivirus software is the range of security functions available.
Basic antivirus products primarily focus on identifying and blocking malicious software. Modern endpoint protection platforms can also investigate suspicious behavior, track attack activity, and support incident response.
CrowdStrike combines these capabilities with cloud-based management and optional security services.
However, traditional antivirus products have also evolved. Many now include behavioral protection, ransomware defenses, and advanced monitoring.
Therefore, organizations should compare specific products and subscription features instead of assuming that every antivirus solution offers only basic protection.
The appropriate choice depends on business size, security requirements, available expertise, and budget.
What Happened During the CrowdStrike Global Outage?
On July 19, 2024, a defective CrowdStrike Falcon content update caused widespread disruption to Windows computers.
Affected devices experienced system crashes, including the Windows Blue Screen of Death. The disruption affected organizations across aviation, banking, healthcare, broadcasting, and other important industries.
Microsoft estimated that approximately 8.5 million Windows devices were affected.
Despite the widespread consequences, the outage was not caused by a cyberattack. It resulted from a faulty security content configuration update.
What Caused the Windows System Failures?
CrowdStrike identified a problem involving a Rapid Response Content update distributed to certain Windows Falcon sensors.
An error in its content validation process allowed problematic configuration data to pass testing. When the affected sensors processed that data, an out-of-bounds memory read led to Windows crashes.
The problematic update was distributed at 04:09 UTC and reverted at 05:27 UTC on July 19, 2024.
Windows devices running affected sensor versions that received the update during this period were vulnerable to the issue. Mac and Linux systems were not affected by this particular incident.
Although the update was reverted relatively quickly, some computers required additional recovery steps because they could not restart normally.
What Changed After the Outage?
The incident demonstrated how a software problem involving widely deployed security technology could interrupt essential services.
CrowdStrike published a root cause analysis and described measures intended to improve its update validation, testing, and deployment procedures.
For businesses, the event also emphasized the importance of recovery planning, controlled update deployment, system backups, and operational resilience.
Security software remains essential, but organizations should prepare for technical failures as well as cyberattacks.
CrowdStrike Products and Developments in 2026
In 2026, CrowdStrike continues to develop its cybersecurity platform beyond endpoint protection.
Its broader portfolio includes identity security, cloud protection, threat intelligence, data protection, and next-generation security information and event management, known as SIEM.
The company has also expanded its focus on artificial intelligence, including tools designed to support security investigations and protect AI-related business systems.
Falcon Next-Gen SIEM helps organizations analyze security information from different systems, while Charlotte AI supports AI-assisted security workflows.
CrowdStrike also remains a publicly traded company under the stock ticker CRWD. Its financial results for the quarter ending July 31, 2026, reported continued growth in annual recurring revenue, a measure of subscription-based business activity. Annual recurring revenue reached $5.84 billion, representing 25% year-over-year growth.
These developments show its continuing emphasis on integrated cybersecurity services, although customers still need to assess the suitability and reliability of individual products.
CrowdStrike Falcon Pricing and Subscription Options
CrowdStrike Falcon pricing depends on the product bundle, billing arrangement, and security capabilities required.
The company’s published US prices, checked in October 2026, include the following annually billed options:
| Product | Published annual price |
|---|---|
| Falcon Go | $59.99 per device |
| Falcon Pro | $99.99 per device |
| Falcon Enterprise | $184.99 per device |
| Falcon Complete | Contact sales |
Falcon Go targets simpler small-business protection needs. Falcon Pro builds on Falcon Go by adding firewall management capabilities, while Falcon Enterprise includes more advanced endpoint detection and response functionality.
Falcon Complete provides managed security services with pricing available through the company’s sales team.
A free trial is also offered for eligible customers. Prices, availability, regional taxes, and included features may change, so buyers should verify current terms before purchasing.
Who Should Consider CrowdStrike Cybersecurity?
CrowdStrike may suit organizations that manage numerous devices, store sensitive information, or require advanced monitoring.
Companies in finance, healthcare, education, technology, and other sectors may benefit from endpoint protection and centralized security management.
Smaller businesses can evaluate entry-level protection bundles, while larger organizations may require advanced threat detection, identity security, or managed response services.
Before choosing a cybersecurity platform, businesses should consider:
- Security requirements: Identify important devices, information, and likely threats.
- IT resources: Determine whether employees can investigate alerts or require managed services.
- Compatibility: Check supported operating systems, existing tools, and deployment requirements.
- Business continuity: Evaluate update controls, recovery procedures, and outage resilience.
- Total cost: Include subscriptions, administration, training, and operational support.
A successful deployment also requires appropriate security policies, employee awareness, reliable backups, and regular system maintenance.
Conclusion
CrowdStrike remains an important company in modern cybersecurity, providing technologies designed to protect businesses against malware, ransomware, compromised identities, and sophisticated cyberattacks.
Its Falcon platform combines endpoint protection, threat intelligence, cloud security, and response capabilities within a broader security ecosystem.
The 2024 global outage highlighted significant operational risks associated with software updates, while the company’s ongoing development reflects the increasing demand for integrated protection.
Organizations considering its services should evaluate both security effectiveness and operational resilience before selecting a suitable solution.
Also Read: Siemless Explained: Complete Guide to Modern Threat Detection
Frequently Asked Questions
What is CrowdStrike used for?
CrowdStrike is used to protect computers, servers, cloud systems, and digital identities from cybersecurity threats. Its Falcon platform provides malware prevention, threat detection, investigation, and response capabilities for businesses and other organizations.
Is CrowdStrike an antivirus?
Yes, CrowdStrike offers next-generation antivirus protection through Falcon Prevent. However, its broader cybersecurity platform also includes endpoint detection and response, identity security, cloud protection, and managed security services.
Why did CrowdStrike cause a global outage?
The July 2024 outage occurred because a defective Falcon content configuration update caused certain Windows systems to crash. It was a software-related failure rather than a cyberattack.
Is CrowdStrike free to use?
CrowdStrike offers a limited free trial, but its commercial security products generally require paid subscriptions. The cost depends on the selected package, number of protected devices, and additional services.
Is CrowdStrike better than Microsoft Defender?
Both offer enterprise cybersecurity capabilities. The better fit depends on an organization’s existing technology, security requirements, licensing arrangements, and response needs. Businesses should compare their specific product versions rather than assuming one is universally superior.
Is CrowdStrike safe to use after the outage?
CrowdStrike continues to provide cybersecurity products and has documented corrective measures following the 2024 incident. However, no security platform is completely free from operational risk. Organizations should assess current product performance, update policies, and recovery procedures before deployment.


One Comment